Configuring a Multi-Server NPS Environment with a Shared Database Server
Overview
This article describes how to set up a deployment with multiple Netwrix Privilege Secure for Access Management servers communicating with a single Postgres server. Instructions are included for configuring TLS for all network traffic to the Postgres server. Optional migration steps are included for users who want to use a Postgres database from an existing Privilege Secure deployment.
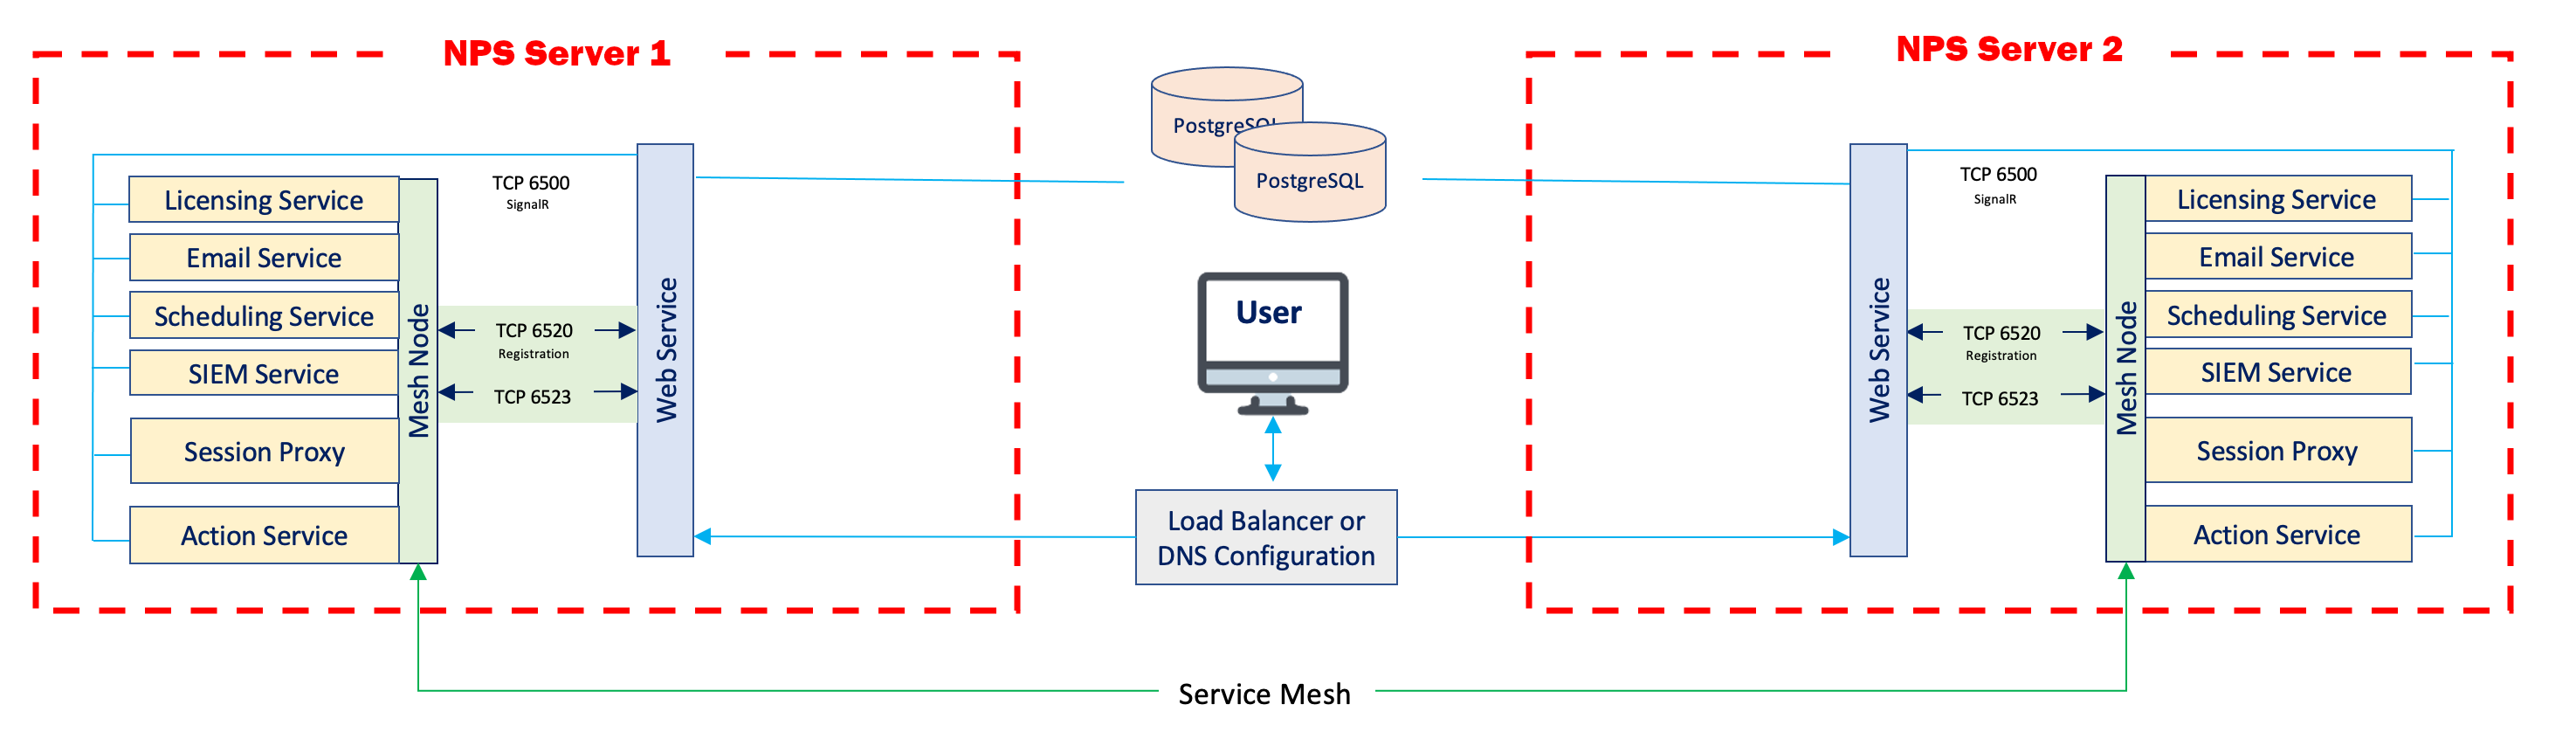
This diagram illustrates the target network architecture.
Instructions
Configuring the Postgres Server
-
On the Postgres server, open the
NPS_Setup.exeinstaller, and install Postgres 12. Next, use theNPS_Setup.exeinstaller to install Privilege Secure. (This is necessary for the Postgres database to be properly configured. There is no need to launch Privilege Secure on the Postgres server at any point in this process, and the Postgres database can be entirely administered from the remote Privilege Secure servers.) -
(Recommended) Now that the Postgres database is properly configured, you can uninstall Privilege Secure on the Postgres server. This conserves disk space and computing resources.
-
Open the
sbpam_node.jsonfile. On a default installation to the C: drive, the file is located here:C:\ProgramData\Stealthbits\PAM\ProxyService\sbpam_node.json -
Ensure that both
localhostand the FQDN of your Postgres server are populated underadvertise:{"advertise": ["testlab-pg01.sbpamtestlab.com", "localhost"],"tags": []} -
Go to the TLS certificate directory. On a default installation to the C: drive, the directory is located here:
C:\ProgramData\Stealthbits\PAM\tls\certs\ -
Copy the
\ProgramData\Stealthbits\PAM\tls\certs\sbpam-node.crtand\ProgramData\Stealthbits\PAM\tls\keys\sbpam-node.pemfiles into the root of the Postgres data directory. On a default installation to the C: drive, the Postgres data directory is located here:C:\ProgramData\Stealthbits\Postgres12(If you want to copy the
.crtand.pemfiles to a subdirectory of the data directory, you must specify their relative subpaths later in these instructions, when configuring thepostgresql.conffile.) -
Open the Certificate Manager. Import the
\ProgramData\Stealthbits\PAM\tls\cacerts\sbpam-region.crtcertificate into the Trusted Root. -
Open the
pg_hba.conffile. On a default installation to the C: drive, the file is located here:C:\ProgramData\Stealthbits\Postgres12\pg_hba.confEdit the file to contain one or more entries that allow connections from your Privilege Secure application servers. For instance, to allow all IP addresses in the
10.2.0.xrange, add an entry ending in/24:host all all 10.2.0.0/24 md5Or, for granular access on a per-IP basis, add a line for each IP address ending in
/32:host all all 10.2.0.1/32 md5host all all 10.2.0.2/32 md5 -
Open the
pg_hba.conffile. On a default installation to the C: drive, the file is located here:C:\ProgramData\Stealthbits\Postgres12\postgresql.conf -
Under
# - SSL -, edit the SSL settings as follows:# - SSL -ssl = on#ssl_ca_file = ''ssl_cert_file = 'sbpam-node.crt'#ssl_crl_file = ''ssl_key_file = 'sbpam-node.pem' -
Restart the Postgres service. Your Postgres server should now be ready to accept TLS-encrypted traffic.
Configuring the NPS Servers
-
On each Privilege Secure server, open the
SB_Setup.exeinstaller, and install Postgres 12. Next, use theSB_Setup.exeinstaller to install Privilege Secure. -
After Privilege Secure is installed, open the
appsettings.jsonfile. On a default installation to the C: drive, the file is located here:C:\Program Files\Stealthbits\PAM\WebEdit this file so that the
Databasekey references the hostname of the Postgres server:"Database": {"Host": "testlab-pg01.sbpamtestlab.com","Port": 5432} -
Obtain a copy of the
\ProgramData\Stealthbits\PAM\tls\cacerts\sbpam-region.crtcertificate from the Postgres server. Open the Certificate Manager. Import thesbpam-region.crtcertificate into the Trusted Root of the local machine.
You should now be able to access the Privilege Secure console at https://[yourNPSServerIP]:6500, and all traffic should be TLS encrypted.
NOTE: If you receive an IIS certificate warning from your browser, install an IIS certificate using Installing an IIS Certificate
Key Export/Import
To ensure that encryption keys are in agreement between Privilege Secure servers, follow the instructions outlined in Configuring Encryption Keys in Multiple NPS Server Environments.