Creating a Service Mesh Between App Servers
Overview
This article describes how to configure a service mesh in Netwrix Privilege Secure for Access Management. Follow these instructions to ensure proper setup and high availability.
Complete the following before configuring a service mesh:
- If you have two application servers with internal PostgreSQL on each, you must configure high availability (HA) before configuring a service mesh. For additional information on the HA setup, see Configuring and Upgrading in High Availability Mode and Using Remote Services Configurations.
- In both PostgreSQL and SQL Server deployments, you must complete the key exchange in your environment before configuring a service mesh. For additional information on the key exchange setup, see Configuring Encryption Keys in Multiple NPS Server Environments.
IMPORTANT: Multi-factor authentication (MFA) should be disabled for the Privilege Secure Administrator account, if used. While this is indicated by an error message when running
sbpam-proxy.exe, the error does not indicate the missing 2FA or the need to disable it before running.
For additional information on used protocols and ports, see Port, Firewall, and Datacenter Requirements.
Instructions
IMPORTANT: When the C drive is referenced, these configuration files are on the C drive. If the application was installed to a dedicated drive, replace X with your appropriate application drive letter for steps with this example.
-
On the primary Privilege Secure server, locate the Web directory. Default path:
C:\ProgramData\Stealthbits\PAM\Web\Copy the entire contents of this directory to the corresponding path on the secondary server.
-
On the primary server, locate the
appsettings.jwt.jsonfile. Default path:C:\ProgramData\Stealthbits\PAM\WebService\appsettings.jwt.jsonIn the primary
.jsonfile, locate theJwtnode. Copy it to theappsettings.jwt.jsonfile on the secondary server.NOTE: The
Jwtnode consists of the contents found within the{}braces followingJwt. Typically, theJwtnode is the only node defined in the file. You can copy the entire file from one server to another, as in the following example.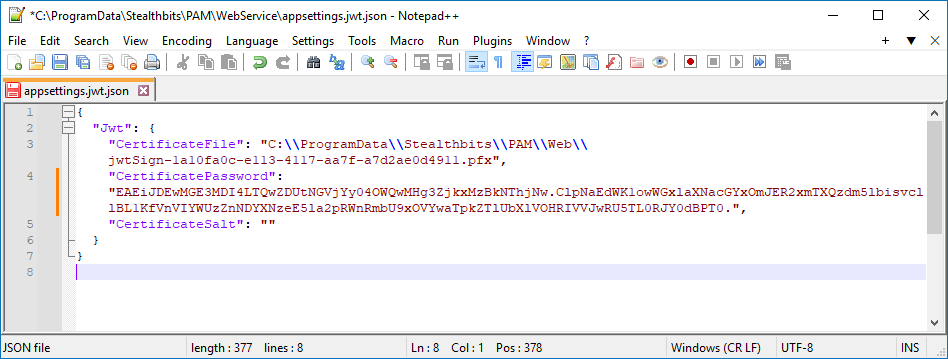
-
Copy the file referenced in
appsettings.jwt.jsonfrom the primary to the secondary server. -
On the secondary server, open IIS Manager and restart the web server.
-
On the secondary server, restart all Privilege Secure services.
-
Start Privilege Secure on the secondary server. Log in, click your User Name in the upper-right corner, and select Settings. Click Register Services.
-
Review the
sbpam_node.jsonfile on both the primary and secondary servers. Default path:C:\ProgramData\Stealthbits\PAM\ProxyService\sbpam_node.jsonThe default
advertisevalue is blank. In theadvertisevalue, specify the IP address, FQDN, and NetBIOS name of the server where thesbpam_node.jsonfile is located. Example:{"advertise": ["192.168.1.123","NPS-PRI.test.lab","NPS-PRI"],"tags": []} -
On both servers, remove the file
sbpam-node.crt. Default path:C:\ProgramData\Stealthbits\PAM\tls\certs\sbpam-node.crtNOTE: The
sbpam-node.crtfile may reappear immediately following deletion. This behavior is expected. -
On the primary server, run the following command in an elevated Command Prompt to obtain the CA hash:
"X:\Program Files\Stealthbits\PAM\ProxyService\sbpam-proxy.exe" register ca-hashCopy the returned hash value and use it in the following step.
-
On the secondary server, run the following command in an elevated Command Prompt to register the server as a cluster on the primary server:
"X:\Program Files\Stealthbits\PAM\ProxyService\sbpam-proxy.exe" register -s <%primary.address%> -u <%admin%> -P Cluster -H <%HASH%>IMPORTANT: Replace the placeholders with corresponding values. The
%admin%value should represent the Privilege Secure administrator account in thedomain\samaccountnameformat. The administrator account used must temporarily have MFA disabled in the Users & Groups section of the Web Interface.The output should resemble the following structure:
Registration successful (remotes: [192.168.1.123:6523], routes: [192.168.1.123:6524]) -
Restart all Privilege Secure services on the secondary node using PowerShell:
Restart-Service SbPAM* -ForceThen restart IIS:
Restart-Service w3svc
Enabling Recording Replication (Optional)
Complete the following steps to enable replication of session recordings (.webm files for web sessions, .iolog files for non-web sessions):
IMPORTANT: This must be done on both servers. The
sbpam_iolog.jsonfile is generated on the C drive regardless of the location from which the command is run.
-
Open a command prompt, go to
X:\Program Files\Stealthbits\PAM\ProxyService, and run the following command to generate the iolog config:sbpam-proxy.exe cfg -c sbpam_iolog -
Open the
sbpam_iolog.jsonfile that has just been created and ensure that a replicas setting exists and is set to 2. Ensure that the resulting file is properly comma-separated. Then, save thesbpam_iolog.jsonfile."replicas": 2 -
After the file is saved, restart the proxy service. Recording replication should occur.
For detailed steps on moving the recording locations, see Changing the Path Where Session Recordings Are Stored.